innerHTML vs textContent — the difference, and why a username can run code
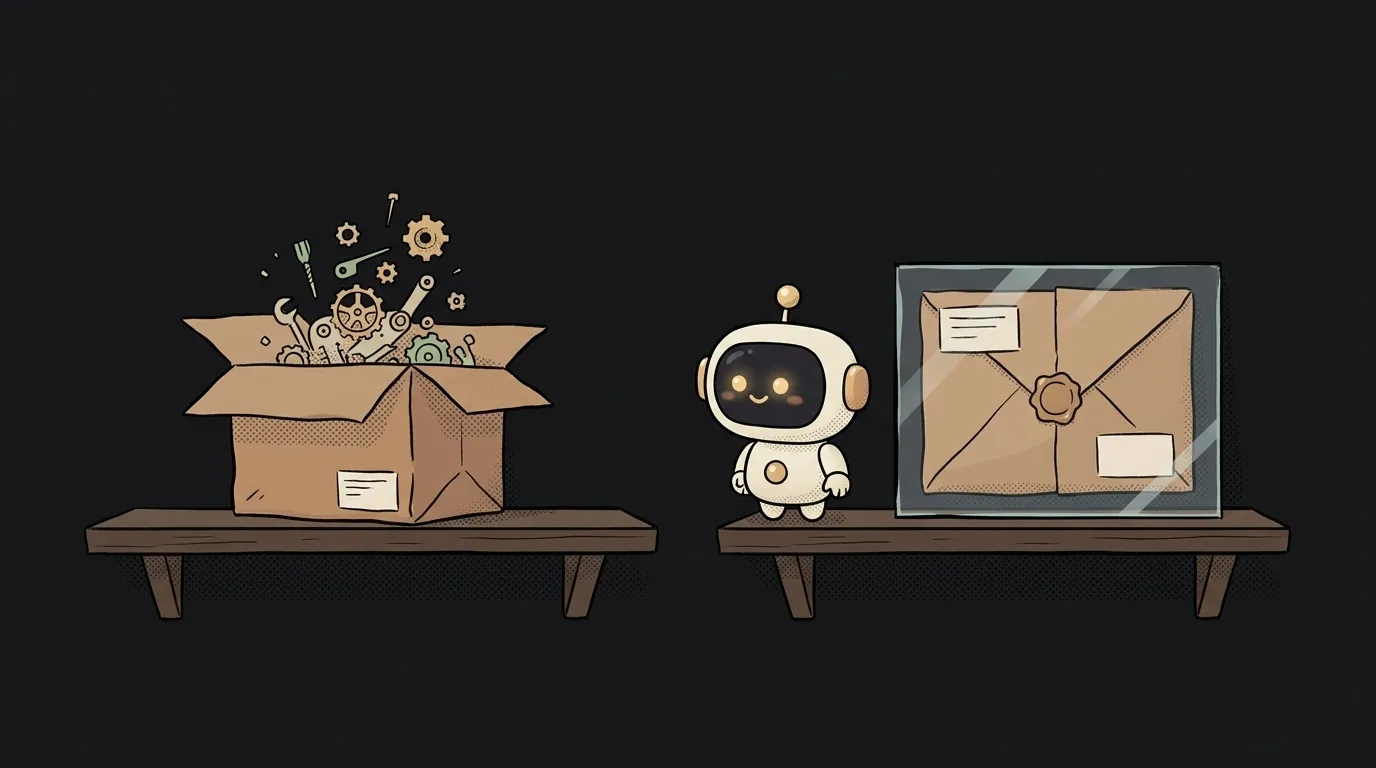
Picture this: your app shows a greeting, "Hi, Anna!" — with the user's name. Someone signs up with this name:
<img src=x onerror="alert('hacked')">
If the greeting is inserted with innerHTML, everyone who sees that name gets a popup. And instead of a popup it could be code that steals their login. If it's inserted with textContent, a strange name in angle brackets just appears on screen. No harm done.
One property instead of the other — and you have a security hole. Let's break down the difference and finish with a verdict that isn't "it depends".
What innerHTML and textContent do
Both properties read and change an element's content on the page. More precisely — a node in the DOM, the live tree of the page the browser builds.
textContent treats text as text. What you put in is what shows up, letter for letter. Angle brackets stay angle brackets.
el.textContent = "<b>Hi</b>"
// on screen: <b>Hi</b>
innerHTML treats the string as a piece of HTML. The browser parses it and builds real elements from it.
el.innerHTML = "<b>Hi</b>"
// on screen: a bold "Hi"
Picture two parcels. The first is displayed under glass: you see the label, but nobody reaches inside. The second is unpacked, and whatever's inside assembles itself and starts working. Great if it's your furniture. Bad if it's someone else's.
Comparison on five criteria
1. What it does with the string.
textContent— shows it as is, parses nothing.innerHTML— parses it as HTML and builds elements.
2. Security.
textContent— safe for any text, even the nastiest.innerHTML— dangerous if anything from outside ends up in the string: a name, a comment, a server response. Attributes likeonerrorwill run foreign code. This attack is called XSS.
3. What happens to the old content.
textContent— everything inside is replaced with one piece of text.innerHTML— the old elements are destroyed and built again. Their click handlers and any text typed into fields disappear with them. Hence the classic bug:list.innerHTML += "<li>…</li>"— and every button in the list stops responding.
4. Speed.
textContent— fast: the browser has nothing to parse.innerHTML— slower: every time it runs the HTML parser. Unnoticeable on a couple of lines, noticeable on long lists.
5. When you need it.
textContent— almost always: names, prices, messages, anything that's just text.innerHTML— when you write the markup yourself, entirely, with no outside data inside.
And what is innerText
There's a third relative — innerText. It also works with text, but it looks at the page through a human's eyes. It doesn't return text hidden with CSS, and it places line breaks the way they appear on screen.
The price is speed: to know what's visible, the browser has to recalculate the page layout. So to write text, use textContent. You rarely need innerText — only when you want exactly what the user sees.
Where AI comes in
Here's a fresh trap. You're building a chat with an AI model, and the answer comes back in Markdown. To make bold text bold, the AI assistant writes: convert Markdown to HTML and insert it with innerHTML.
But the model's answer is outside data too. If someone slips the model a crafty instruction, it can return <img onerror=…> in its answer. That's called prompt injection, and through innerHTML it turns into a breach.
The fix is to run the HTML through a sanitizer like the DOMPurify library before inserting it. It cuts out scripts and dangerous attributes but keeps bold text and lists. If you're building such a chat with the guide on streaming AI responses, add one line to your prompt: "sanitize HTML with DOMPurify before innerHTML".
Who should use what
The verdict:
- Use
textContentby default. For 95% of tasks — showing a name, a number, a message — it's the right and only tool you need. - Use
innerHTMLonly if the HTML is entirely yours: a card template with no data plugged in. Or if the data went through DOMPurify. innerText— for reading only, when "how it looks on screen" matters.
And in React the choice is made for you. Writing {name} in the markup works like textContent — safely. The dangerous option is deliberately given a scary name: dangerouslySetInnerHTML. If you see it in AI-written code, check where the data comes from.
Can you insert a script with innerHTML?
A <script> tag inserted with innerHTML isn't executed by the browser. But that doesn't save you: code runs through attributes like onerror on an image. So you have to guard against all HTML, not just the script tag.
Why did my buttons stop working after innerHTML +=?
Because += rebuilds all the content from scratch: the old buttons are removed and new ones are created without click handlers. Add elements with append or insertAdjacentHTML instead.
The AI Architect 2027 course: step by step from computer basics to your own app and first customers. 543 short lessons on your phone.
Read next

Ed25519 vs RSA — which SSH key to choose in 2026

What is sudo — and why it asks for your password, not the admin's

What is a tar.gz file — and why a tar archive can be bigger than the files

What is a command-line flag — and why git commit -ma breaks but -am works

scp or rsync — and why rsync sent 141 bytes instead of two megabytes the second time
