#security

Ed25519 vs RSA — which SSH key to choose in 2026
Ed25519 or RSA for your SSH key: which is faster, shorter and safer, why an old RSA key suddenly stops letting you in, and which ssh-keygen command to type.
What is a checksum — and how to check a file downloaded intact
What a checksum is in plain words: how SHA-256 works, how to verify a downloaded file on any system, and what this check will not protect you from.
localhost vs 0.0.0.0 — the difference, and how one flag opens your server to the network
localhost vs 0.0.0.0 explained: how to open a site from your phone, why Next and Docker listen on the whole network by default, and which address to pick.
What is a prototype in JavaScript — and why an empty object isn't empty
What a prototype is in JavaScript: where objects get properties you never added, why a word counter breaks on “constructor”, and why __proto__ is risky.
What is a template literal in JavaScript — and why a pair of parentheses opens an SQL injection
What template literals in JavaScript are: backticks, ${} interpolation, tags like sql`` — and the one mistake that turns a safe query into an SQL injection.
What is a random number in programming — and why a computer can't roll a die
What a random number is in code and how Math.random works: why it's pseudo-random, where the Math.round trap hides, and when you need crypto instead.
innerHTML vs textContent — the difference, and why a username can run code
innerHTML vs textContent: what's the difference and which to use. A five-criteria comparison, how innerHTML opens a hole for foreign code, and where innerText fits.
Why CSP blocks my own scripts — three causes and how to fix each
"Refused to execute inline script" and the site is dead. Why CSP blocks your own scripts: the three common causes, how to check each one, and what to change.
What is an open redirect — and why a link on your domain lands on someone else's site
An open redirect is a hole you add yourself with a next parameter on the login form. How your own domain becomes a phishing link, and the three ways to fix it.
What is a TLS certificate — and why it now lives 200 days instead of a year
A TLS certificate proves a domain, not the owner's honesty. What's inside a certificate, who signs it, and why the maximum lifetime is being cut to 47 days.
What is CSP (Content Security Policy) — and why it blocks your own script first
CSP isn't a filter for bad code, it's an allowlist of sources. What Content Security Policy is, why it blocks your own scripts, and how to turn it on safely.
SSL vs TLS — what the difference is and what you're actually buying
SSL was banned back in 2015, yet the word lives on in price lists and configs. The difference between SSL and TLS, which versions are alive, and what to enable.
How to add security headers to your site — in one evening, without breaking it
Step by step: how to add security headers — nosniff, HSTS, Referrer-Policy, frame-ancestors and CSP in report mode — with ready configs and a way to verify.
What Is a Third-Party Script — and Why Someone Else's Line on Your Page Sees Everything
Chat, analytics and pixels are someone else's code with your code's rights. What third-party scripts are, how they slow a site, and how to tame them.
What is XSS — and why an attack doesn't need a script tag
XSS is someone else's JavaScript running for your users. Where it comes from, why an image tag is enough, and what actually closes the hole.
What is SQL injection — and why the surname O'Brien breaks your site
SQL injection is when text from a form becomes a command for your database. We use an apostrophe in a surname to show why «stripping quotes» never works.
What is CSRF — and why your browser attaches your session for free
CSRF is an attack where another site sends the request and your own browser attaches the cookie. The mechanics, what SameSite covers, and why you need a token.
What attackers type into your form — 6 strings to test your own app with
Six strings worth typing into your own form: what should happen, and what it means if something else does. A five-minute self-check for holes.
How to validate user input — 6 steps the AI skips
A step-by-step walkthrough: how to validate form data on the server — schema, allowlist, normalization and limits. With code and human error messages.
What is 3-D Secure — and why it's not extra friction but a transfer of liability
3-D Secure is payment confirmation on the customer's bank side. Who pays for a fraud dispute after 3DS, when it's mandatory, and what the friction costs.
What is secure storage — and why an app doesn't know its own key
Secure storage is a safe inside your phone: the key never leaves the chip, and the app itself can't read it. Keychain, Keystore, and where not to put a token.
What is a refresh token — and why you sometimes get logged out everywhere
A refresh token is the long key you trade for a short pass. Why apps use two tokens instead of one, and why the server sometimes logs you out on every device.
What is a passkey — and why it can't be stolen from the server
A passkey is a login without a password: the site only stores a public key. Here's how your phone signs you in and why phishing stops working.
Passkeys or passwords — what to choose when building login from scratch
Passwords are stored as hashes, passkeys as public keys. Compared on leaks, phishing, recovery and convenience — and a verdict on what to ship in a new project.
What not to paste into an AI chat — 7 things that leave your computer
What not to send to an AI: keys, other people's personal data, NDA documents. And why "training is off" doesn't mean "nobody will ever read this".
What is app signing — and why a lost key is worse than lost code
You can rewrite code; you can't rewrite a signing key. What app signing is, how an upload key differs from Google's key, and how not to lose everything.
Why .gitignore isn't working — and why .env still ended up on GitHub
Why .gitignore isn't working: usually the file is already tracked, so the rule has no effect. Three real causes, a one-command check, and the fixes.
What is a proxy server — and why your API key is public without one
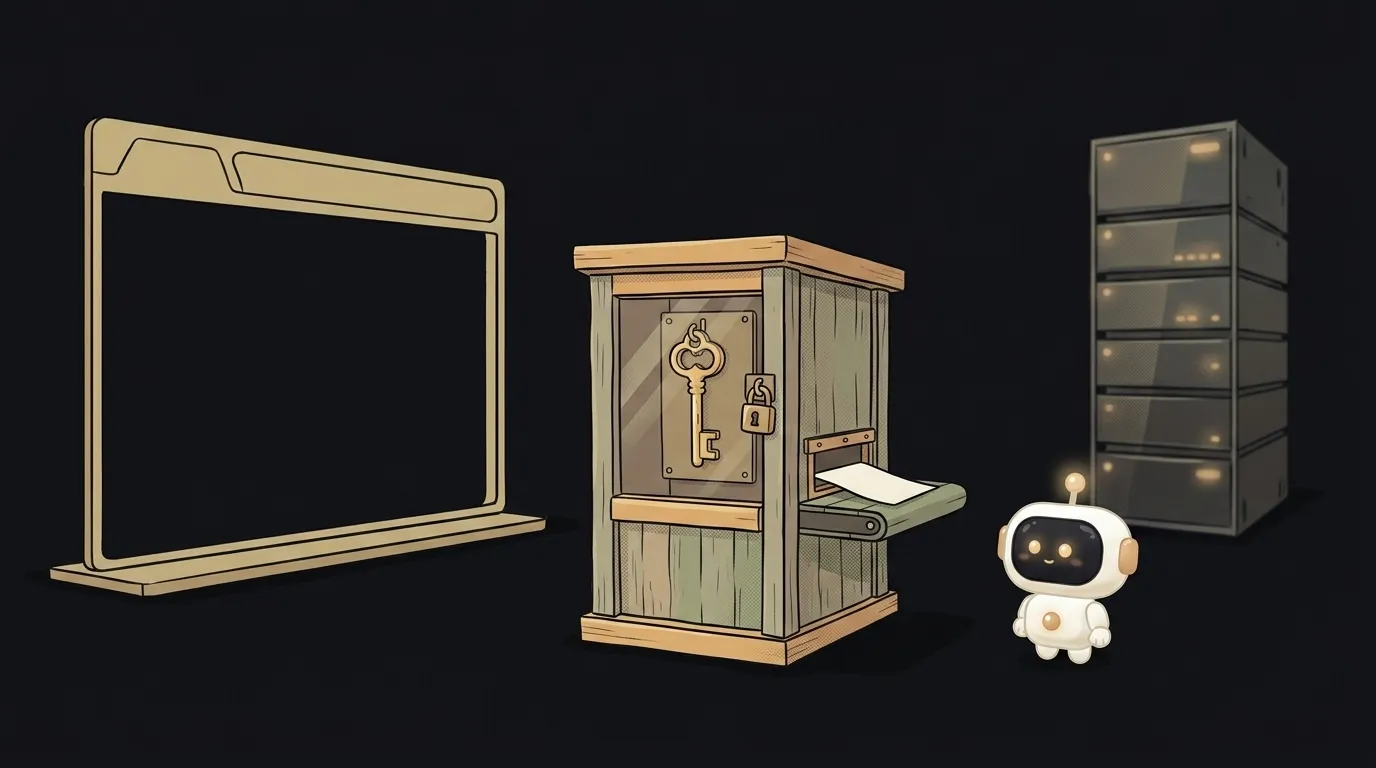
A proxy is a middleman between your app and someone else's service. What a proxy server is, forward vs reverse, and why your API key needs one.
What is encryption — and why the browser padlock doesn't protect your database
Encryption hides data in a way you can undo. Here's what the padlock in your browser actually protects — and what it doesn't.
Red flags in AI-generated code — 7 things to check before you ship
AI code breaks where things are boring, not where they're hard. Seven places worth a look before your users find them for you.
What is RLS — and why your table is open to the whole internet
Your database key sits right in your site's code — by design. What protects you is RLS: what it is, why it's easy to miss, and how to write your first policy.
What is a webhook signature — and why without one your bot believes any lie
A webhook signature proves the request came from Stripe and not from a prankster. How it works, why you need it, and why plain JSON parsing breaks it.
What is a hash — and why your password can't be turned back
What a hash is in plain words: why a service that emails you your old password can't be doing it honestly — and where the password actually goes.
Password, magic link or email code — which login to pick
Three ways to log people in, compared on cost, safety and hassle. With a table, a straight verdict — and the non-obvious thing that kills magic links.
How to add user roles — admin and regular, with no hole in access
A role that lives only in the UI isn't a role: the button is hidden, the request still works. Step by step, add user roles that actually can't be bypassed.
What is an AI jailbreak — and how it differs from prompt injection
A jailbreak is talking a model into breaking its own rules. Don't confuse it with prompt injection. Here's what an AI jailbreak is and why it's so hard to close.
What is an API key — and why a leak hits your wallet
An API key is a pass to someone else's service, used in your name. Here's what an API key is, where it lives, why it can't sit in your code, and how to store it safely.
What are AI guardrails — and why a prompt isn't security
Guardrails are checks around the model, not a 'don't do that' line in the prompt. Here's why a wall holds where a request gets talked around so easily.
What is 2FA — and why it saves you even after your password is stolen
2FA is a second key to your account that changes every 30 seconds. Here's why it holds even when your password has long leaked into someone else's database.
How to store API keys safely — and why a frontend .env isn't a secret
The classic beginner mistake: hiding a key in a frontend .env. At build time it lands in the bundle and anyone can see it. Here's how to store API keys properly.
Pre-launch security checklist — 7 checks you can do in an evening
Before you publish an app, 7 checks are enough to not hand your data and money to the first passing bot. A concrete list, no lecturing.
What is prompt injection — and why a single email can 'command' your AI
Prompt injection is when text the model is merely reading gets executed as a command. Here's why it happens and how to defend against it.